Extended Detection and Response (XDR)
WatchGuard ThreatSync Core
Accelerate Threat Detection and Response with Unified XDR.
The Problem: Fragmented Security and Overloaded Teams
Every day, security teams fight threats with tools that don’t talk to each other. Firewalls see one thing. Endpoints another. Cloud apps something else entirely.
The result? Gaps, noise, and missed threats, while attackers move faster than ever.
Whether you’re a security engineer, an IT director, or a business decision maker, the challenge is the same: how to see the full picture of risk without adding complexity, cost, or burnout.
The Solution: One Unified View of Every Threat
WatchGuard ThreatSync Core unifies detections across your entire WatchGuard security stack, firewall, endpoint, and identity, into a single pane of glass.
It automatically correlates events, scores incidents by risk, and orchestrates responses, so you can detect, prioritize, and respond faster than ever before.
Beat the Threat Uncertainty with Unified Visibility
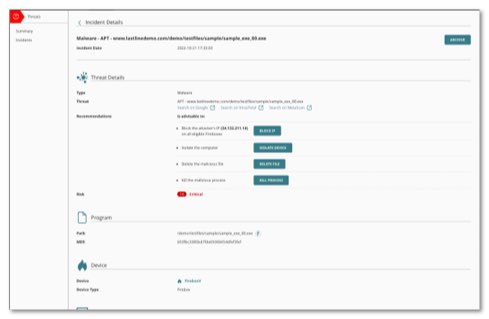
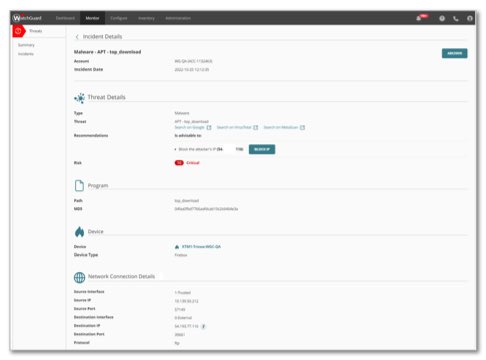
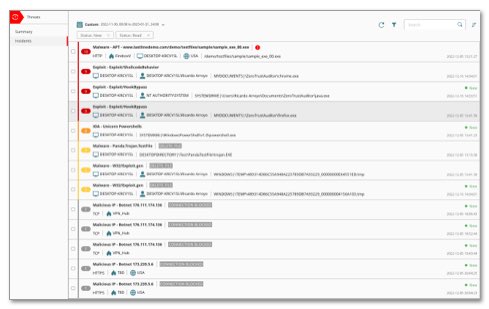
Tired of chasing disconnected alerts from different consoles? ThreatSync pulls every alert, log, and detection into one place, automatically correlating data from WatchGuard’s full security stack.
- A complete view of threat activity across endpoints, networks, and users
- Context on how detections relate to one another (cross-detections)
- A faster path from alert to action, all in one intuitive dashboard
No more console-hopping. No more guesswork. Just clarity, confidence, and speed.
Give Time Back to IT with Smart Incident Prioritization
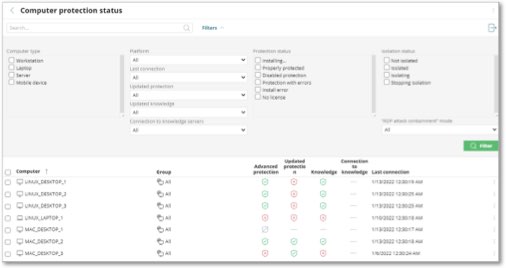
Every alert feels urgent, but not every alert matters. ThreatSync uses AI-driven scoring and correlation to rank incidents by true business risk.
That means your team can immediately see:
- Which threats need action now
- Which ones are already contained
- Where the biggest vulnerabilities are hiding
Instead of drowning in alerts, your engineers focus on what counts, saving time, energy, and sanity.
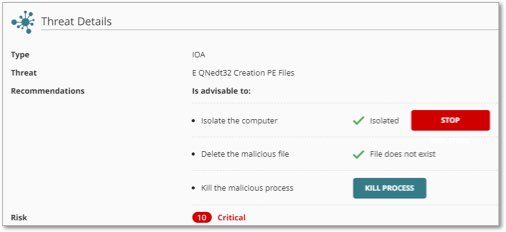
Respond Faster. Contain Smarter.
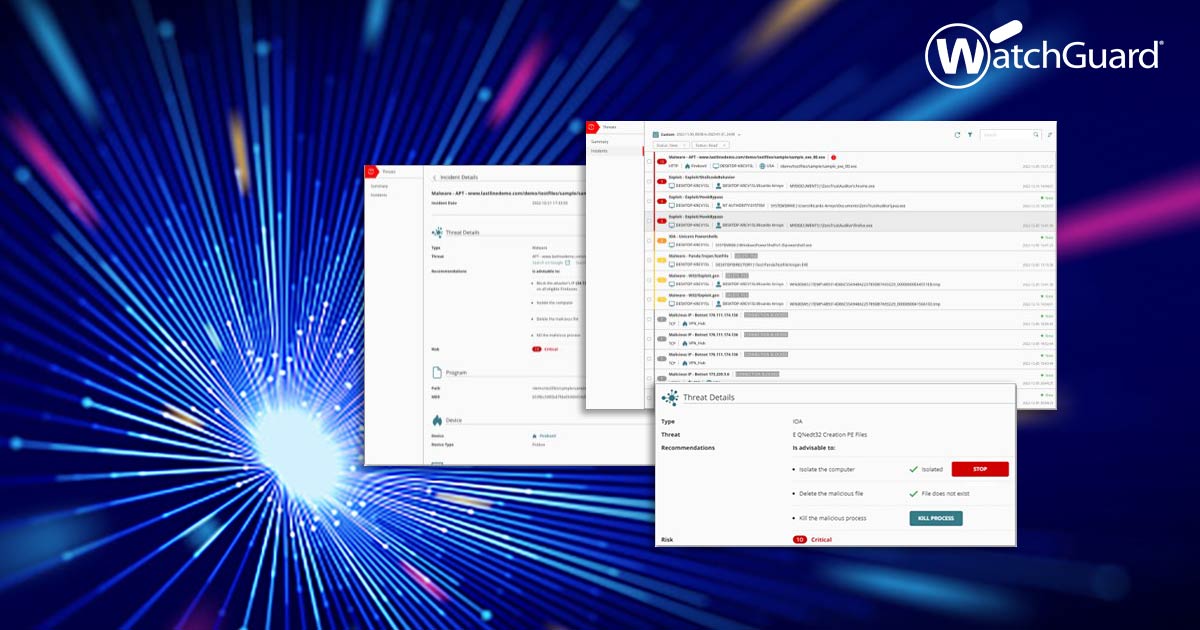
When a threat hits, seconds count. ThreatSync automates the heavy lifting of investigation and response.
- Detect threats earlier (reduced MTTD)
- Orchestrate response actions across your environment
- Contain attacks automatically or on demand
With ThreatSync, your team can stop attacks before they spread, and get back to business faster.
Minimize Damage with Targeted Remediation
When an attack happens, knowing where to act first makes all the difference. ThreatSync gives responders the intelligence they need, instantly, to isolate compromised systems and automate remediation at the source.
- Quicker containment
- Less downtime
- Measurable cost reduction
Built-In, Not Bolted-On
With WatchGuard, ThreatSync Core is included at no extra cost inside WatchGuard Cloud and the Total Security Suite. You get enterprise-grade visibility and automation, without enterprise-grade complexity or price tags.
Upgrade to Total Security Suite
Scale When You’re Ready: Upgrade to ThreatSync+ NDR
Need deeper insight across your network and cloud layers? ThreatSync+ NDR extends your view beyond endpoints, detecting anomalies and lateral movement before damage occurs.
Upgrade seamlessly: no rip-and-replace. Just more visibility, more intelligence, and more control.
Explore ThreatSync+ NDR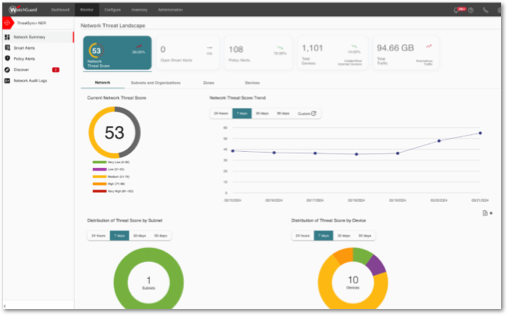
Designed for Every Type of Security Decision Maker
| If You’re a… | ThreatSync Helps You… |
|---|---|
| CISO or IT Director | Get unified visibility and faster threat containment without new headcount |
| Security Engineer | See cross-domain telemetry in one dashboard and automate response actions |
| Business Owner or MSP | Reduce cost, complexity, and downtime with a single, integrated security layer |
The Proof Behind the Platform
- 100s of billions of events analyzed
- 2.1 billion binaries classified
- Millions of adversary movements tracked
- Thousands of zero-day threats blocked
ThreatSync isn’t theoretical. It’s working behind the scenes every day to stop real-world attacks, across organizations of every size.
Key Benefits at a Glance
Greater Visibility
Complete insight across endpoints, networks, and users
Comprehensive Security
Unified detection and automated response across your WatchGuard stack
Faster Remediation
AI-driven incident scoring cuts investigation time dramatically
Automated Response
Contain and remediate threats automatically to reduce MTTR
No Added Cost for XDR
Included with WatchGuard Cloud and Total Security Suite
Why It Matters
“ThreatSync finally gives our team the clarity we were missing. We see every threat in one place, and act on it immediately.”
Ready to See XDR in Action?
Take a test drive of WatchGuard ThreatSync in WatchGuard Cloud, or speak with your WatchGuard Partner today to see how unified XDR can transform your defense strategy.